Why do AI-built apps stay live when nobody uses them?
On 27 October 2026 Lovable, a tool that builds apps from a plain description, published a blog post about "undead apps". These are the projects nobody touches anymore. A prototype from a hackathon, a short coding marathon, an internal tool built by a colleague who left in the spring, the page for a campaign that ended. According to Lovable, many are still published and connected to data, and the problem affects every AI tool.
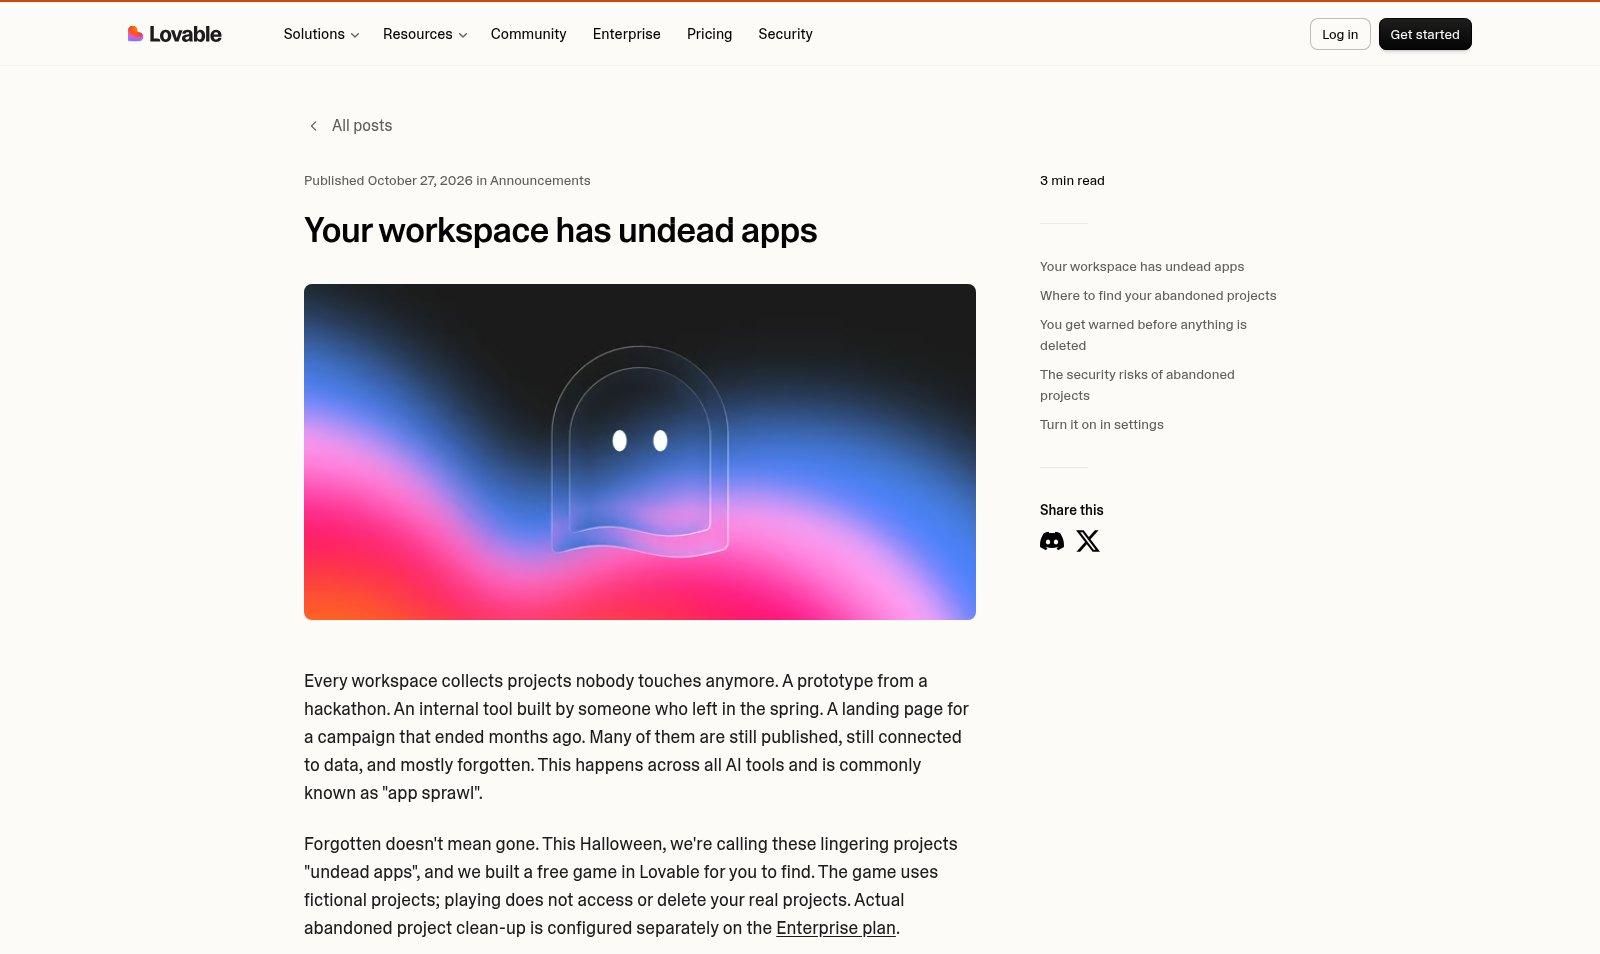
For customers on its Enterprise plan, Lovable now marks a project as abandoned after 60 days without activity. If the admin chooses, the project is deleted after a grace period, with warnings to the people working on it and 60 days to recover it. This is a vendor feature, and we cite it as an example of a shutdown rule, not as an independent study.
The problem has an older name, shadow IT. The UK's National Cyber Security Centre describes it as tools used for work that nobody has recorded. Its examples include code kept in unmanaged repositories and AI services used with company data. It rarely comes from bad intentions. Usually someone was trying to get their job done with what they had.
What do you risk with a forgotten app?
Lovable lists four risks, and they apply to any tool.
- Access still open. The demo built for a client meeting still accepts logins, and the key created for a test still opens the company system.
- Flaws never fixed. The event sign-up form relies on a component that got a security update, but nobody installed it.
- Data kept for no reason. Last year's waitlist still holds names, emails and answers, while the GDPR says personal data should be kept only as long as its purpose needs.
- No owner. The person who built the attendance tracker moved teams, and nobody checks who gets in anymore.
This is not hypothetical. Escape, a company that sells security testing, analysed more than 5,600 public apps built with these tools. It found 175 cases of exposed personal data, including bank details and medical records. According to Escape, most of the flaws were visible without logging in.
Step one: how do you list the apps built with AI?
Start from the subscriptions. Ask whoever manages them which app-building tools are active in the company, then ask each team what they built with them. For an organisation of around 20 people or fewer, the NCSC says a spreadsheet kept up to date by hand is enough. For each app, write down the following.
- Name and web address, and whether it is public or internal only.
- Who built it and for what job, for example the quote request form or the shift calendar.
- What data it touches, such as customers, staff or payments.
- Which systems it connects to, and with which keys.
- The last time someone used it for work, not the last time it was opened.
Step two: who owns each app?
Every app needs a person who answers for it, by name. They don't need to code. They need to know what the app is for, who uses it and when it can be switched off. When they change role or leave the company, the handover includes their apps, just like the laptop and the passwords.
Replit, a Lovable competitor, offers a different route for changes to a company's main software. Someone non-technical asks an AI agent for the change, but the result goes through developer review before it goes live. The principle is the same. Anyone can propose, and a person approves.
Step three: when do you shut down an idle app?
You need a written rule, the same for every team. Lovable uses 60 days without activity as its default. You can pick another number, as long as you decide it in advance. When an app crosses that line, the shutdown always follows the same steps.
- Warn the owner and the users, with a shutdown date.
- Export the data you still need and delete what you no longer need.
- Revoke keys, passwords and connections to other systems.
- Take the app offline and record the shutdown in the list.
Our read: there is one detail people often miss. Lovable warns that when a project is deleted, its web address is freed up and someone else can take it. If that address went out in emails or flyers, whoever opens it tomorrow may find a page that isn't yours. Before you shut an app down, check where you published it.
What changes if you are a public body or a NIS entity?
For many companies and public bodies the list is also an obligation. NIS entities are the companies and public bodies that EU cybersecurity law treats as essential or important. The baseline measures that Italy's National Cybersecurity Agency (ACN) sets for them include an up-to-date inventory of services, systems and software applications, custom ones included. An AI-built app used for work belongs in that inventory. The deadline to adopt the measures depends on when the entity was added to the NIS list.
What about us?
We apply the same discipline to the AI agents we build, and we describe it on our Security page. An agent reaches only the systems that job needs, with permissions that can be revoked. Changes are tracked and reversible, and actions stay in a log. A forgotten app is the opposite, because nobody knows what it touches and nobody switches it off.
What do you do with each app on the list?
- If nobody has used it for two months and it holds no personal data, shut it down following the steps.
- If it touches customer or staff data and nobody owns it, find an owner now or switch it off.
- If people use it every day and it carries real work, treat it as company software, with backups, controlled access and updates.
- If it was an experiment that is over, export what you need and delete the rest.
“Building an app now takes an afternoon. Switching it off takes someone who remembers it exists.”
DBrothers — how we keep agents and apps under control
Open a spreadsheet and write down the AI-built apps you know about, with the name of the person who owns each one. If the owner column has gaps, we can start there together and decide which apps to keep and which to switch off.